
A professional networking platform runs on something more valuable than profiles, feeds, job listings, or messages: trust. Members need reasonable confidence that the person behind a profile is genuine, their account cannot be easily hijacked, private conversations will not become an uncontrolled spam channel, and professional information will not be exposed beyond the audience they intended.
That makes platform security different from simply adding encryption or placing a security badge on a login page. Trust has to exist across the entire product: registration, identity, authentication, profile visibility, connections, messaging, blocking, reporting, administrator permissions, integrations, data retention, and account deletion.
The stakes are particularly high in professional communities. A compromised entertainment account may create inconvenience. A compromised professional identity can be used to impersonate an executive, approach employees, contact clients, send fraudulent opportunities, collect sensitive business information, or damage a member’s professional reputation.
For founders and platform operators, the important question is therefore not simply, “Is our platform secure?” A more useful question is: where does trust need to exist, what could break it, and what controls should the product provide when something goes wrong?
Key Takeaways
- Professional networking platform security begins with trustworthy identity, not just infrastructure.
- Account protection should cover authentication, risky logins, session control, account recovery, and privileged administrator access.
- Messaging requires its own safety model because spam, phishing, impersonation, unwanted outreach, and malicious links often appear inside legitimate platform communication.
- Privacy should control what information is collected, who can see it, why it is used, how long it remains, and how members exercise data rights.
- Moderation works best when reports, investigations, actions, appeals, and administrator activity are recorded as structured workflows.
- Security is an operating system for trust—not a feature that can be added after the network has already grown.
Why Trust Is Core Infrastructure for a Professional Networking Platform
Professional networks create interactions that can have real economic and career consequences. Members use them to find employees, evaluate candidates, build partnerships, communicate with prospects, discover suppliers, share credentials, join industry communities, and develop professional relationships.
The value of those activities falls quickly when identity becomes unreliable. If profiles are easy to impersonate, messages are dominated by spam, credentials cannot be trusted, or members cannot control who sees their information, the network may continue growing numerically while becoming less useful professionally.
This is why trust should be treated as a product architecture decision. Verification, authentication, blocking, permissions, moderation, auditability, privacy settings, and abuse controls all influence whether members are comfortable using the network for meaningful professional activity.
The requirements can become even more important in specialized communities. An alumni network may need to verify affiliation. A healthcare community may need stronger professional-credential checks. A trade association may restrict certain resources to active members. A supplier network may verify organizations before allowing access to buyer opportunities. Miracuves explores this broader concept in its guide to trust and membership design in niche professional networks.
The Five-Layer Trust Model: Identity, Accounts, Messaging, Privacy, and Governance
A useful way to evaluate platform safety is to divide trust into five connected layers. Each solves a different problem, but weaknesses in one layer can undermine the others.
| Trust Layer | Main Risk | Important Controls | Operator Question |
|---|---|---|---|
| Identity | Impersonation, fabricated credentials, duplicate or deceptive profiles | Email verification, organization checks, credential workflows, profile review, identity state | How do we establish that a professional identity is credible enough for this community? |
| Account Protection | Account takeover, stolen credentials, weak recovery | MFA, session controls, login throttling, risk-based checks, secure recovery | What happens when credentials are stolen or a session becomes suspicious? |
| Messaging | Spam, phishing, scams, harassment, mass outreach | Rate limits, reporting, blocking, outreach boundaries, link/attachment controls | How do we preserve useful communication without creating an abuse channel? |
| Data Privacy | Overexposure, unnecessary collection, uncontrolled sharing | Visibility controls, consent, minimization, retention, export/deletion workflows | Can members understand and control how their professional information is used? |
| Governance | Inconsistent moderation, excessive admin access, untraceable decisions | Role-based administration, audit logs, report lifecycle, appeals, escalation | Can the operator investigate and act without creating new security risks? |
A mature platform connects these layers. A member who reports an impersonation attempt, for example, may trigger identity review, account restrictions, message investigation, moderator action, notification workflows, and an appeal process. Treating each security feature as an isolated toggle makes those incidents much harder to manage consistently.
Identity Trust: Prove What Matters Without Collecting Too Much
Identity is the starting point because professional networking relies on attribution. A recommendation only matters when the person giving it is credible. A recruiter message only carries value when the recruiter can be associated with a real organization. An employment claim becomes more meaningful when there is supporting context around the company, duration, credential, or verification state.
Separate account identity from professional profile information
The authentication account and the public professional profile should not be treated as the same data object. Login credentials, verification status, account state, recovery information, and security events serve one purpose. Employment history, skills, qualifications, projects, publications, location, and career preferences serve another.
Separating them makes privacy and security easier to reason about. A member may update a job title or hide career preferences without changing authentication state. Likewise, disabling an account should not require rewriting every professional relationship associated with the profile.
For teams planning the underlying architecture, the Miracuves guide to professional networking database design and the professional social graph explains why identity, privacy, blocking, moderation, and audit data should be considered in the original schema rather than retrofitted later.
Verification should match the risk of the network
Not every platform needs government-document verification. The appropriate level depends on what members can do and what happens when identity is false.
- A public career community may only need verified email and anti-spam controls for most members.
- An alumni community may verify institutional affiliation.
- A professional association may validate membership numbers or qualifications.
- A marketplace-oriented network may verify organizations before enabling commercial outreach.
- A sensitive expert community may require manual approval or stronger identity proofing for particular roles.
The goal is proportional trust. Collecting more personal information than the platform actually needs can increase privacy risk without necessarily improving network quality.
Design for impersonation disputes
Verification cannot prevent every fake profile, so the platform also needs an operational answer for impersonation. Members should be able to report an account, identify the reason, provide supporting context where appropriate, block further contact, and receive a clear indication that the report entered a review process.
Operators need more than a generic support inbox. They need a structured record connecting the reported profile, reporting member, reason, supporting evidence, investigator, action, timestamps, and appeal state. That creates consistency and makes repeated abuse easier to recognize.
Account Protection: Make Account Takeover Hard and Recovery Safe
Even a perfectly genuine professional profile can become dangerous if an attacker gains control of it. Established accounts are particularly attractive because they already contain connections, reputation, employment history, and message access.
Account protection therefore has to assume that passwords may eventually be guessed, reused, phished, leaked elsewhere, or exposed through unsafe devices.
Use stronger authentication where risk justifies it
Multi-factor authentication should be available to members and strongly considered for administrators, moderators, recruiters, organization owners, and other privileged roles. Platforms serving higher-risk audiences can also consider phishing-resistant authentication methods such as passkeys or security keys rather than depending only on passwords and manually entered codes.
Security-sensitive actions should be treated differently from routine browsing. Changing the primary email address, resetting authentication factors, creating a new administrator, exporting large amounts of member data, or altering payment and organization ownership information may justify re-authentication or additional verification.
Detect suspicious login behavior without punishing normal users
Login throttling, failed-attempt monitoring, unusual-device signals, new-location alerts, suspicious session behavior, and member notifications can provide additional protection. These controls should be designed carefully so attackers cannot deliberately lock large numbers of legitimate users out of the service.
Make sessions visible to members
A practical account-security page can show active sessions or recognized devices, approximate login context, recent security events, and the ability to revoke sessions. This gives members a way to respond when something looks unfamiliar rather than forcing them to contact support for every concern.
Treat account recovery as authentication
Recovery is often the weakest path into an otherwise well-protected account. An attacker who cannot defeat MFA may instead try to reset the account, change the registered email address, socially engineer support, or replace an authentication factor.
Recovery workflows should therefore be designed with the same seriousness as login. Sensitive recovery events should be logged, users should be notified when important security settings change, and privileged accounts may need stronger recovery procedures than ordinary members.
Messaging Safety: Protect Professional Communication Without Killing Utility
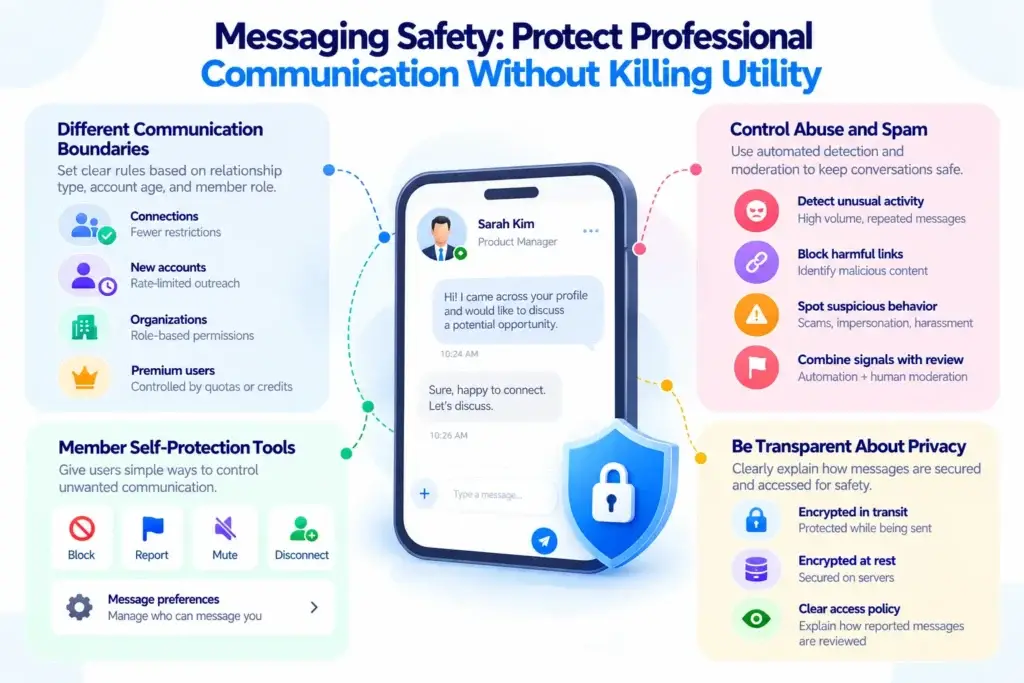
Messaging creates enormous value in a professional network because it converts discovery into action. A connection becomes an introduction. A profile view becomes a recruiting conversation. A supplier search becomes a commercial discussion.
It is also one of the easiest areas to abuse.
Common problems include unsolicited bulk outreach, recruitment scams, malicious links, impersonation, harassment, automated prospecting, repeated contact after rejection, deceptive job offers, and accounts that build credibility before switching to abusive behavior.
Different relationships should have different communication boundaries
A useful platform does not need to treat every message identically. Messaging between established connections may have fewer restrictions than first-contact outreach. Communication from newly created accounts may be rate-limited. Organization representatives may have role-specific permissions. Premium outreach can be controlled through quotas or credits rather than becoming unlimited by default.
Miracuves’ professional networking feature architecture provides an example of this principle through metered outreach, message records, member roles, and operator controls. The important trust principle is not the commercial model itself; it is that communication outside an established relationship should have explicit boundaries that the operator can observe and adjust.
Members need immediate self-protection tools
Block, report, mute, disconnect, message-request controls, and communication preferences reduce dependence on centralized moderation. If somebody receives unwanted contact, the safest first action should not require waiting for an administrator.
Build spam and abuse controls around behavior
Operators can monitor signals such as unusually high message volume, repeated identical content, rapidly increasing connection requests, excessive link sharing, large numbers of blocks or reports, and new accounts attempting high-volume outreach.
No single signal proves abuse. A recruiter may legitimately contact many candidates. An event organizer may connect with hundreds of professionals after a conference. The platform should therefore combine signals, account history, role context, and human review instead of treating one threshold as universal proof of wrongdoing.
Do not promise message privacy the architecture does not provide
Platforms should clearly distinguish encrypted transport, encrypted storage, and end-to-end encrypted messaging. These are not interchangeable claims. If administrators need access to reported conversations for abuse investigations, the product should explain how that workflow operates rather than marketing every message as inaccessible to the service itself.
Data Privacy: Give Members Clear Control Over Professional Information
Professional profiles can contain extensive personal information: employment history, education, skills, certificates, location, contact details, professional interests, job preferences, connections, messages, search activity, applications, recommendations, and organization relationships.
The privacy challenge is not simply preventing a database breach. It is ensuring that information is collected and exposed for understandable purposes.
Collect less when less is enough
Data minimization reduces both privacy exposure and operational complexity. If the platform does not need a particular piece of personal information to deliver a feature, founders should question why it is being collected.
This becomes especially important with identity verification. A platform may need to know that a qualification was verified without retaining every document used to establish it indefinitely.
Visibility should be granular
Privacy is easier to understand when users can control meaningful categories instead of facing one global public/private switch.
- Profile visibility
- Contact information visibility
- Connection-list visibility
- Profile-view history
- Job-search or opportunity preferences
- Messaging permissions
- Activity and feed visibility
- Organization affiliation
- Search-engine indexing where applicable
The defaults matter as much as the settings. A privacy control that technically exists but is hidden behind several menus does little to build member confidence.
Map every third-party data flow
Analytics platforms, authentication providers, email services, push notifications, payment gateways, applicant-tracking integrations, CRM systems, cloud storage, and customer-support tools may all receive or process some platform information.
Before launch, operators should know which systems receive data, what data is sent, why it is required, where responsibility sits, and what happens when an integration is removed.
Plan retention, export, correction, and deletion early
Account deletion is rarely as simple as deleting one row. The member may have posts, comments, connections, job applications, company roles, reports, moderation records, subscription history, messages, endorsements, audit events, or legal records attached to the account.
The platform therefore needs an explicit data-lifecycle policy: which information can be deleted, which should be anonymized, which must remain for security or legal reasons, and how users can request access or correction where applicable.
Privacy and regulatory obligations vary by jurisdiction and operating model. Technical workflows can support data-rights and consent requirements, but final compliance depends on the applicable laws, the platform’s actual data processing, contracts, integrations, and appropriate legal review.
Moderation and Governance: Build a Trust System Operators Can Actually Run
A platform can have excellent member-facing safety controls and still fail operationally if administrators lack a clear governance system.
The moderator needs to know what was reported. The investigator needs relevant account and activity context. The operator needs a history of what action was taken. The affected member may need an appeal path. Senior administrators may need escalation capabilities without giving every moderator unrestricted access to billing, user exports, system configuration, or other sensitive areas.
Separate the report, investigation, action, and appeal
These should not be one generic status field. A report is an allegation. An investigation is a review process. A moderation action is an operator decision. An appeal challenges that decision.
Keeping those stages distinct makes the system more auditable and reduces the chance that a mistaken or incomplete report automatically produces an irreversible punishment.
Use role-based administrative access
A trust-and-safety moderator should not automatically have access to financial configuration. A billing operator should not necessarily be able to read member reports. A support representative may be able to inspect account status without being able to change privileged roles.
Role-based access limits the damage that can result from compromised administrator credentials, internal mistakes, or unnecessary privilege.
Keep an administrative audit trail
High-impact actions should leave records showing who performed the action, when it occurred, what object or account was affected, and—where practical—why the action was taken.
Auditability is particularly important for account suspensions, privilege changes, organization ownership transfers, privacy overrides, data exports, moderator decisions, security-setting changes, and bulk administrative operations.
Technical Security: Protect APIs, Sessions, Data, and Administrative Access
Trust-and-safety workflows depend on secure technical foundations. A well-designed reporting interface cannot compensate for an API that lets one member retrieve another member’s private information simply by changing an identifier.
Important engineering areas include secure authentication, server-side authorization, session management, protected API endpoints, encrypted data transfer, secure secret management, careful file-upload handling, dependency management, database access controls, backups, monitoring, and vulnerability remediation.
Authorization matters as much as authentication
Authentication answers, “Who is this user?” Authorization answers, “What is this user allowed to do with this specific resource?” Professional networks contain many relationship-dependent permissions, so the second question is frequently harder.
A recruiter may view information that an ordinary member cannot. A company administrator may manage one organization but not another. A moderator may inspect a report without receiving unrestricted access to private data. A blocked member should lose pathways that would otherwise expose the blocker’s information.
Treat administrator accounts as higher-risk identities
Administrator access can expose many accounts at once, making privileged identities disproportionately valuable to attackers. Strong authentication, shorter or carefully controlled sessions, re-authentication for sensitive actions, least-privilege roles, security-event logging, and restricted export capabilities are sensible foundations.
Plan for failure rather than assuming perfect prevention
No security architecture can promise that incidents will never occur. The more useful question is how quickly the platform can detect abnormal behavior, restrict compromised accounts, revoke sessions, investigate events, restore services, communicate with affected parties when necessary, and learn from the incident.
Security Across the Product Lifecycle: What Must Happen Before and After Launch
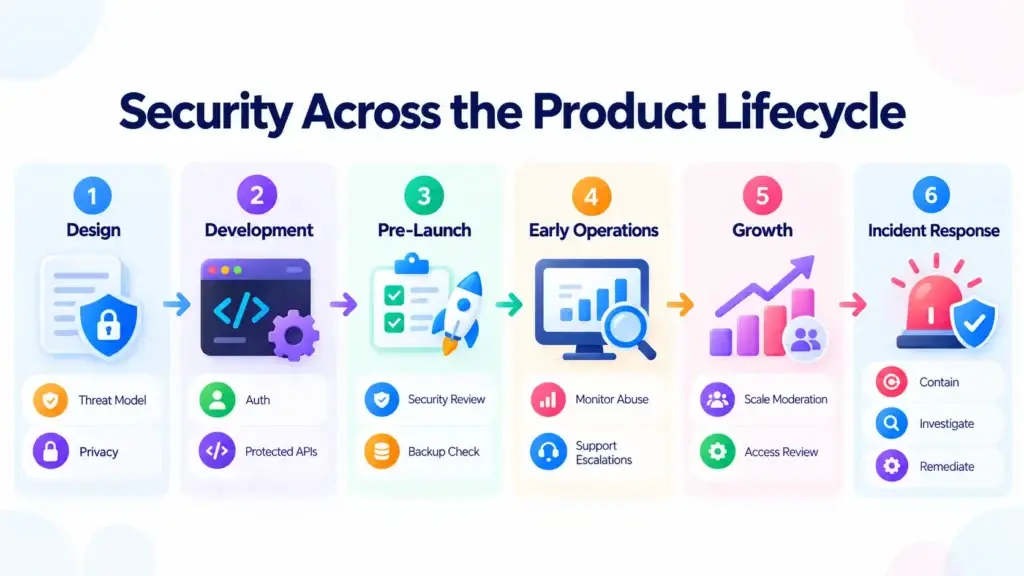
| Stage | Trust and Security Priorities |
|---|---|
| Product Design | Threat modeling, identity model, privacy defaults, roles, messaging boundaries, reporting workflows, data minimization |
| Development | Secure authentication, server-side authorization, protected APIs, validation, secret handling, audit events, safe integrations |
| Pre-Launch | Security review, access review, backup testing, recovery checks, privacy review, abuse scenarios, administrator training |
| Early Operations | Monitor login abuse, spam patterns, reports, moderation workload, false positives, support escalations and risky integrations |
| Growth | Scale moderation, tune rate limits, introduce stronger verification where necessary, improve automation, review privileged access |
| Incident Response | Contain affected accounts, preserve relevant records, rotate credentials where needed, investigate, communicate and remediate |
The practical point is that security does not end at deployment. Member behavior changes, attackers adapt, new integrations are added, roles become more complex, and the network begins producing abuse patterns that were impossible to predict from a small test environment.
What Founders Should Verify Before Choosing a Professional Networking Platform Foundation
Founders evaluating a ready-made or custom platform should avoid reducing security due diligence to a single question such as, “Is the app secure?” Instead, ask for evidence about the specific controls that matter to the planned operating model.
- How are authentication, verification, sessions, and account recovery handled?
- Can privileged roles be separated rather than sharing one universal administrator account?
- Are reports, moderation decisions, and appeals recorded?
- Can members block other users immediately?
- Can messaging and connection activity be rate-limited or governed by relationship type?
- How are private fields protected at the API level?
- Can users control meaningful profile-visibility settings?
- How are exports, corrections, retention, and deletion handled?
- Which third-party services receive member data?
- Can security-sensitive administrator actions be audited?
- Who owns the source code and can your own technical team inspect it?
- What happens when vulnerabilities, dependencies, or integrations need updating after launch?
Teams still evaluating implementation approaches can also review Miracuves’ guide on how to evaluate a professional networking platform development partner. The important distinction is that vendor selection should follow the product’s trust requirements—not replace them.
Founder Decision Signals
Identity Risk
If false credentials, impersonation, or unauthorized membership would materially reduce the value of your network, verification must be designed into the product from the beginning.
Communication Risk
If members can contact people outside established relationships, build outreach limits, blocking, reporting, and message-abuse controls before growth makes them difficult to retrofit.
Privacy Risk
If profiles contain employment, credential, location, contact, applicant, or commercial data, define visibility and retention before collecting the information.
Operational Risk
If several staff members will manage users, reports, subscriptions, organizations, or content, separate administrative permissions and keep auditable records of sensitive actions.
How Miracuves Helps Founders Build Trust Into a Professional Networking Platform
Security becomes much easier to operationalize when trust controls are part of the product foundation instead of being treated as unrelated additions after launch. Identity states, permissions, moderation records, messaging controls, administrator roles, privacy workflows, and auditability all influence one another.
Miracuves provides a ready-made professional networking platform solution for founders who want to begin with an established product foundation rather than rebuilding profiles, networking, hiring, messaging, governance, and operator workflows from zero.
For applicable ready-made deployments, Miracuves offers a 6-day deployment path with source-code ownership, branding, and administrative control. That deployment speed should not be confused with a universal compliance guarantee: privacy policies, third-party integrations, security configuration, organization-specific controls, and jurisdictional legal requirements still need to be aligned with the actual launch model.
The founder advantage is therefore not simply moving faster. It is beginning with a product foundation where the trust model can be reviewed, configured, extended, and operated deliberately.
Related reading: healthcare app security guide.
Final Thoughts: Trust Has to Work Before the Network Can Scale
A professional network becomes valuable when people are willing to attach their real reputation, career history, relationships, conversations, and opportunities to it. That willingness depends on trust.
The strongest security strategy is therefore not a long list of isolated technical controls. It is a connected operating model: credible identity, protected accounts, controlled communication, privacy-conscious data handling, reliable reporting, role-based administration, auditability, and an incident process that assumes problems will occasionally occur.
Founders who design those layers before growth have more room to adapt. They can tighten verification when the community demands it, adjust messaging boundaries when spam patterns appear, refine privacy defaults, add specialist moderation roles, and expand governance without rebuilding the entire platform underneath active members.
That is what trust architecture ultimately provides: not a promise that nothing will ever go wrong, but a platform that knows what should happen when identity, access, communication, privacy, or behavior no longer looks trustworthy.
FAQs
What makes a professional networking platform trustworthy?
Trust comes from several connected layers: credible member identity, secure authentication, controlled messaging, transparent privacy settings, blocking and reporting, consistent moderation, role-based administrator access, and auditable security operations. No single feature establishes trust by itself.
Does every professional networking platform need identity verification?
No. Verification should match the network’s risk and purpose. A general professional community may only require verified email and anti-abuse controls, while regulated or credential-based communities may need organization, membership, qualification, or stronger identity checks.
How can a professional networking platform reduce account takeover risk?
Useful controls include multi-factor authentication, secure account recovery, login throttling, session management, suspicious-login monitoring, re-authentication for sensitive actions, member security notifications, and stronger protections for administrator accounts.
How should messaging safety work in a professional network?
Messaging safety should combine relationship-based permissions, reasonable outreach limits, blocking, reporting, spam signals, abuse monitoring, link and attachment safeguards, and operator review. Communication outside an established connection can have stricter controls than normal member-to-member conversations.
What privacy controls should professional networking platforms provide?
Useful controls include profile visibility, contact-information visibility, connection visibility, messaging preferences, activity settings, data export or correction workflows, account deletion processes, retention rules, and clear disclosure of third-party data sharing. Exact legal obligations depend on the jurisdiction and operating model.
Why are role-based admin permissions important?
Different staff members need different levels of access. Moderators, billing teams, support staff, organization managers, and system administrators should not automatically receive the same permissions. Least-privilege roles reduce the impact of compromised accounts and operational mistakes.
Can trust and security controls be added after launch?
Some controls can be improved later, but identity, permissions, privacy, blocking, moderation, audit records, and data lifecycle rules influence the underlying architecture. Designing them early is usually safer and less disruptive than retrofitting them after the platform has accumulated users and data.
Miracuves is an independent software development company. We are not affiliated with, connected to, sponsored by, or endorsed by any company or product named in this article.
Terms such as “X Clone” are used descriptively. It is how the software industry refers to building a platform with functionality comparable to a known service, and how clients search for it.
The entire design and codebase of our products is built by our own team. Our products contain no code, design, graphics, or content originating from any third-party website or applications.
All third-party names and marks referenced in this article are the property of their respective owners, referenced solely to identify the services discussed.