Key Takeaways
- B2B travel booking platform security should protect agent accounts, corporate travel data, supplier connections, payments, wallets, credit limits, refunds, and administrative controls.
- Role-based access should ensure agents, accountants, support users, corporate administrators, suppliers, and finance teams receive only the permissions required for their responsibilities.
- Financial actions such as wallet adjustments, credit-limit changes, refunds, commissions, and payouts should use controlled permissions and durable audit records.
- Supplier API credentials should remain server-side, while supplier responses, payment callbacks, and booking data should be validated before they affect platform records.
- Strong authentication, organization-level data isolation, privileged-action monitoring, secure webhooks, offboarding controls, backups, and incident procedures should form part of the platform’s security foundation.
Security Signals
- Privileged users should have stronger authentication, session controls, login protection, and step-up verification for high-impact actions.
- Corporate accounts require backend-enforced organization isolation so employees cannot access another company’s bookings, billing information, or travel records.
- Wallets, credit limits, commissions, settlements, and refunds should use ledger-style records rather than silently overwriting financial balances.
- Supplier credentials should be securely stored, separated between environments, rotated when necessary, and never exposed through frontend or mobile application code.
- Security monitoring should watch for unusual booking volume, repeated failed logins, rapid wallet depletion, large refunds, unexpected permission changes, and mass data exports.
Real Insights
- B2B travel security is about protecting business authority as much as protecting data; changing a credit limit, refund, commission, or supplier setting can have significant operational consequences.
- A support employee may need to view refund status without having permission to issue the refund, demonstrating why access should be based on specific responsibilities.
- Payment authorization and supplier confirmation should remain separate states so failed or suspicious transactions can be investigated without ambiguity.
- Security controls should extend across the full lifecycle, including employee offboarding, webhook verification, development environments, backups, monitoring, and compliance processes.
- The strongest security approach is: secure identities → enforce role permissions → isolate corporate data → protect financial records → secure supplier APIs → verify payments and callbacks → audit privileged actions → monitor activity → remove stale access → test recovery procedures.
Security in a B2B travel booking platform is more complicated than protecting traveler passwords and payment screens.
A trade-focused travel platform may allow agents to book on behalf of customers, corporate administrators to manage employee travel, finance teams to review statements, suppliers to update inventory, and operators to control commissions, refunds, credit limits, and settlements.
That creates a much wider trust boundary.
For founders who want to understand the complete booking and partner journey before exploring the security layers, this guide explains how a B2B travel booking platform works across traveler, agent, supplier, corporate, payment, and booking workflows.
One compromised traveler account may expose one person’s itinerary. A compromised agent account can potentially expose multiple customer bookings. A compromised corporate administrator account may reveal employee travel records. A leaked supplier credential may affect inventory, pricing, or booking operations across thousands of searches.
That is why B2B travel booking platform security should be designed around identity, permissions, financial controls, API protection, monitoring, and accountability.
The goal is not to make every user an administrator with a different dashboard. The goal is to ensure that each role can access only the data and actions needed for its job.
Why B2B Travel Security Is Different From Consumer Booking Security
A consumer travel account usually controls one person’s profile, payment methods, bookings, saved travelers, and loyalty information.
A B2B account can control far more.
An agent may be able to:
- Search trade inventory
- Book for customers
- Use prepaid balance
- Access a credit limit
- Apply markup
- View commission
- Download statements
- Request cancellation
- Initiate refunds
- Manage sub-agents
A corporate administrator may be able to:
- Add employees
- Create departments
- Define travel policies
- Approve trips
- View company bookings
- Review invoices
- Access expense records
- Control corporate payment methods
A supplier may manage:
- Inventory
- Availability
- Rates
- Policies
- Booking information
- Settlement records
The security model therefore needs to protect both data and business authority.
Someone who gains access to a privileged account may not need to steal data to cause damage. Changing a credit limit, refund destination, supplier rate, commission setting, or account role can be enough.
Security Layer 1: Protect Agent Accounts With Strong Authentication
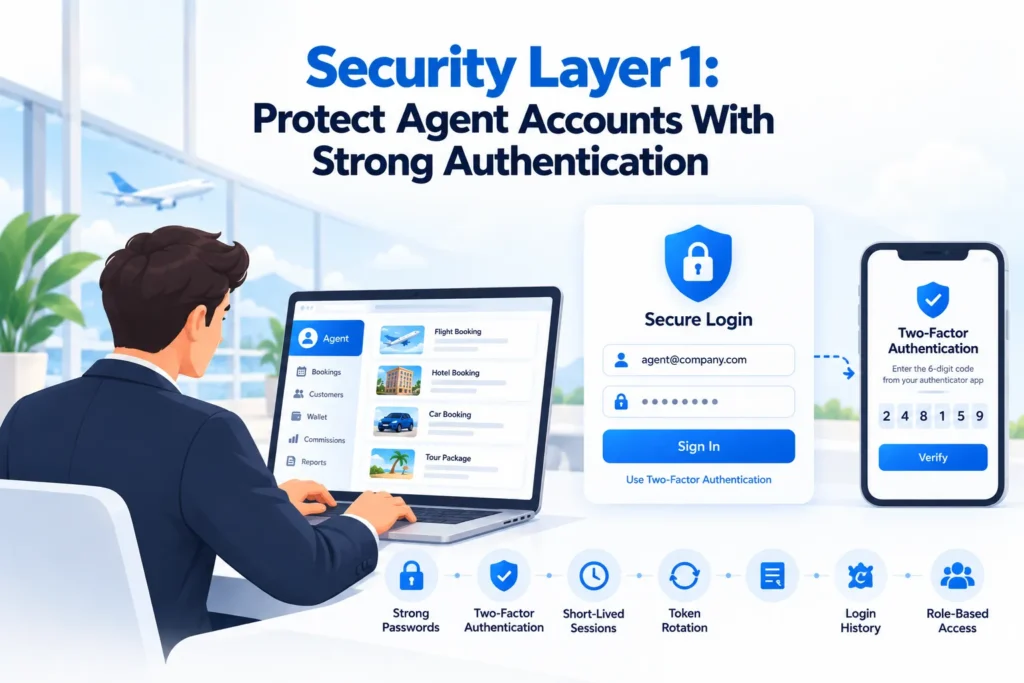
Agent accounts deserve stronger controls than ordinary browsing accounts because they may carry financial authority.
A travel agent account can potentially access:
- Customer information
- Booking history
- Wallet funds
- Credit balances
- Commission records
- Cancellation tools
- Supplier rates
- Statements
At minimum, authentication should support:
- Strong password requirements
- Hashed password storage
- Two-factor authentication for privileged users
- Short-lived authenticated sessions
- Refresh-token rotation where applicable
- Session revocation
- Login history
- Failed-login throttling
- Password reset protection
Founders defining agent permissions, corporate dashboards, supplier access, wallets, commissions, statements, and administrative controls can review these agent and corporate travel features when mapping which functions require stronger authentication and role restrictions.
For high-risk roles such as finance administrators, refund operators, or master agents, additional verification may be appropriate before sensitive actions.
Step-up authentication
A user who is already logged in should not automatically be allowed to perform every financial action.
The platform can require additional verification when someone:
- Changes payout details
- Raises an agent credit limit
- Issues a large refund
- Creates a new administrator
- Changes commission rules
- Exports sensitive records
- Changes supplier credentials
This is often called step-up authentication.
It adds friction only where the potential impact justifies it.
Security Layer 2: Use Role-Based Access Instead of One Powerful Agent Account
Not everyone working inside a travel agency needs the same permissions.
A larger agency might have:
- Agency owner
- Booking agent
- Sub-agent
- Accountant
- Supervisor
- Customer support employee
Giving everyone full access increases risk.
A role-based access model can separate permissions such as:
| Role | Typical Access |
|---|---|
| Agency Owner | Team management, balances, commissions, statements, booking controls |
| Booking Agent | Search, customer booking, booking history |
| Accountant | Statements, invoices, settlement records |
| Sub-Agent | Limited bookings and assigned customer records |
| Support User | Booking visibility without unrestricted financial controls |
Permissions should be explicit.
For example, a support employee may need to see whether a booking was refunded but should not automatically have permission to issue the refund.
Security Layer 3: Protect Agent Wallets, Credit Limits, and Commission Records
B2B travel businesses often involve more than direct card checkout.
Agents may operate with:
- Prepaid wallet balances
- Credit limits
- Deposits
- Commission balances
- Settlement cycles
- Booking margins
That means the financial ledger becomes a security-sensitive system.
Every balance-changing event should create a durable record.
A ledger entry might include:
- Account
- Booking reference
- Transaction type
- Amount
- Currency
- Previous balance
- New balance
- Operator or system action
- Timestamp
- Payment reference
- Reason
The platform should avoid simply overwriting a wallet balance.
Because credit limits, wallet balances, commissions, statements, and settlements directly affect both revenue and security, founders can review the B2B travel platform business model to understand where financial controls fit into the broader operating model.
If the current number changes from 100,000 to 80,000, finance teams should be able to understand exactly which transactions created that change.
Protect credit-limit changes
Credit limit adjustments should require controlled permissions.
The system should record:
- Who changed the limit
- Previous amount
- New amount
- When it changed
- Reason
- Approval where required
For larger B2B businesses, maker-checker workflows can be useful: one authorized person creates a change, and another approves it.
Security Layer 4: Separate Corporate Accounts and Employee Travel Data
Corporate travel platforms hold sensitive business information.
A corporate account may contain:
- Employee names
- Work email addresses
- Employee identifiers
- Department information
- Travel itineraries
- Booking history
- Approval records
- Expense records
- Corporate billing information
- Travel policy data
Users from one company should never be able to access records belonging to another organization.
The authorization layer must check organization ownership on every relevant request.
Do not rely only on frontend filtering.
A hidden menu item is not access control.
The backend should enforce whether the user belongs to the organization and whether their role can access that specific resource.
Security Layer 5: Build Corporate Travel Permissions Around Job Responsibilities
Corporate travel commonly involves multiple roles:
- Employee traveler
- Travel coordinator
- Department approver
- Finance user
- Corporate administrator
Their permissions should differ.
For a broader view of the traveler, agent, corporate, supplier, booking, payment, and admin workflows that need these permissions, this guide covers the B2B travel booking features commonly used across the platform.
Corporate Travel Access Control by Role
| Role | What They May Need | What Should Stay Restricted |
|---|---|---|
| Employee | Create or view personal trips, traveler profile, policy information. | Other employees’ trips, company-wide billing, policy administration. |
| Approver | Review assigned trip requests and approval history. | Unrelated departments, financial administration, platform settings. |
| Travel Coordinator | Book for authorized employees and manage permitted itineraries. | Company financial controls unless separately authorized. |
| Finance | Invoices, expenses, transaction records, corporate settlement. | Supplier credentials and unrelated platform administration. |
| Corporate Admin | User roles, policies, departments, reporting, company settings. | Platform-wide operator settings belonging to the OTA owner. |
Security Layer 6: Protect Supplier API Credentials on the Server
Supplier integrations are among the most sensitive components in a travel platform.
Supplier systems may expose:
- Inventory
- Availability
- Contracted rates
- Booking endpoints
- Cancellation endpoints
- Supplier account identifiers
- Booking references
API keys, secrets, credentials, and signing information should not be embedded in frontend JavaScript or mobile application code where they can be extracted.
The safer pattern is:
Traveler/Agent → OTA Backend → Supplier Adapter → Supplier API
The backend holds the credentials and controls which operations are sent to the supplier.
Supplier credentials should be
- Stored securely
- Separated from source code where practical
- Accessible only to authorized services
- Rotated when needed
- Revoked when compromised
- Different between development and production environments
- Logged carefully without exposing secret values
Production credentials should not be reused casually in test systems.
Security Layer 7: Validate Supplier Responses Instead of Trusting Them Blindly
External APIs should be treated as untrusted inputs.
Even legitimate supplier systems can return:
- Unexpected fields
- Empty values
- Changed formats
- Expired sessions
- Duplicate responses
- Errors
- Inconsistent currencies
- Price changes
The platform should validate supplier responses before those values become booking records.
Validation may include:
- Expected schema
- Currency
- Price
- Availability
- Cancellation conditions
- Supplier reference
- Booking status
- Required traveler fields
This protects the platform from both malicious manipulation and normal integration failures.
Security Layer 8: Use Controlled Booking and Payment States
A secure booking system should not rely on one generic “success” state.
A B2B platform may need to distinguish:
- Booking created
- Credit reserved
- Payment pending
- Payment verified
- Supplier confirmation pending
- Confirmed
- Failed
- Cancellation requested
- Refund pending
- Refunded
- Settlement pending
- Settled
These states matter because financial actions depend on them.
For example, agent commission should not necessarily be treated as final before booking confirmation.
Similarly, a payment authorization should not automatically prove that a supplier reservation exists.
Keeping these states separate makes suspicious or failed transactions easier to investigate.
Security Layer 9: Secure Refunds, Cancellations, and Manual Overrides
Privileged financial actions deserve additional controls.
Examples include:
- Manual refunds
- Partial refunds
- Cancellation fee overrides
- Credit adjustments
- Wallet credits
- Commission corrections
- Supplier payout adjustments
- Manual booking confirmation
These actions should create audit records.
Depending on risk, platforms can also use:
- Approval thresholds
- Dual authorization
- Step-up authentication
- Permission restrictions
- Reason codes
- Supporting notes
The objective is accountability.
Finance and operations teams should be able to reconstruct who changed what and why.
Security Layer 10: Protect Admin and Finance Accounts More Aggressively
Admin users can often access the most sensitive areas of a travel business.
A compromised admin account could potentially:
- Create users
- Change roles
- Modify commissions
- Alter credit limits
- Issue refunds
- Change supplier settings
- View financial data
- Export records
Admin and finance roles should therefore use stronger controls.
Practical measures can include:
- Two-factor authentication
- Shorter sessions
- Device/session visibility
- Re-authentication for critical actions
- IP or environment restrictions where appropriate
- Detailed audit logs
- Limited number of privileged users
- Regular permission reviews
Founders should follow the principle of least privilege: give each user only the permissions needed for the role.
Security Layer 11: Log Privileged Actions, Not Just Logins
Login logs are useful, but they tell only part of the story.
A B2B travel platform should also log actions such as:
- Role changes
- Credit-limit changes
- Wallet adjustments
- Refund approval
- Commission changes
- Supplier credential changes
- Payout changes
- Booking overrides
- Corporate policy edits
- Data exports
A useful audit record includes:
- Actor
- Action
- Resource
- Time
- Previous value
- New value
- Reason where applicable
Logs should themselves be protected against unauthorized modification.
Security Layer 12: Monitor for Unusual Agent and Corporate Activity
Fraud prevention is not only about stolen cards.
B2B platforms can experience account misuse.
Signals worth monitoring may include:
- Sudden increase in booking volume
- Large credit-limit usage
- Multiple failed logins
- New device followed by financial changes
- High refund volume
- Repeated cancellations
- Rapid wallet depletion
- Unusual geographic login pattern
- Mass data exports
- Multiple permission changes
A signal does not automatically mean fraud.
It means the activity may deserve additional review.
Security Layer 13: Protect Corporate Data During Employee Offboarding
One overlooked security risk is former employees retaining access.
When an employee, travel coordinator, finance user, or corporate administrator leaves the company, access should be removable quickly.
A useful offboarding workflow should:
- Disable login.
- Revoke active sessions.
- Remove privileged roles.
- Reassign pending approvals.
- Preserve legitimate audit history.
- Review API or integration credentials owned by that user.
- Confirm that exported data is handled according to company policy.
The same applies when a travel agency removes a sub-agent.
Old accounts should not remain active indefinitely.
Security Layer 14: Keep Payment Data Exposure as Small as Possible
Travel platforms process valuable transactions.
Where possible, sensitive card information should be handled through reputable payment providers rather than stored directly by the booking application.
The OTA should still protect:
- Payment references
- Transaction IDs
- Wallet balances
- Refund records
- Invoices
- Corporate billing data
- Settlement records
Security controls can include:
- Encrypted data transfer
- Tokenized payment flows where supported
- Server-side verification
- Duplicate-payment protection
- Secure webhooks
- Refund authorization
- Audit trails
Payment security responsibilities depend on the selected gateway, architecture, jurisdiction, and operating model.
Security Layer 15: Secure Webhooks and Supplier Callbacks
Travel booking platforms often depend on asynchronous callbacks.
Examples include:
- Payment confirmation
- Supplier booking updates
- Refund status
- Cancellation confirmation
A webhook endpoint should not trust every incoming request automatically.
Useful controls can include:
- Signature validation where supported
- Secret verification
- Timestamp checking
- Replay protection
- Idempotency
- Payload validation
- Source restrictions where practical
- Logging
Without these safeguards, attackers may attempt to forge status updates or repeatedly trigger the same transaction.
Security Layer 16: Separate Development, Testing, and Production
Development environments should not casually use real customer information or live supplier credentials.
Maintain clear separation between:
- Development
- Staging/testing
- Production
Production access should be limited.
Testing environments can use:
- Test accounts
- Sandbox supplier credentials
- Synthetic traveler data
- Payment sandbox environments
This reduces the chance that experimental code or broad developer access exposes live business data.
Security Layer 17: Back Up What the Business Actually Needs to Recover
Backups should be designed around business continuity.
Important records may include:
- Users
- Corporate accounts
- Agent accounts
- Bookings
- Financial ledgers
- Supplier configuration
- Policies
- Statements
- Audit records
- Content
Creating backups is not enough.
Organizations should also test restoration.
A backup that cannot be restored when needed provides little protection.
Security Layer 18: Treat Compliance as an Operating Process
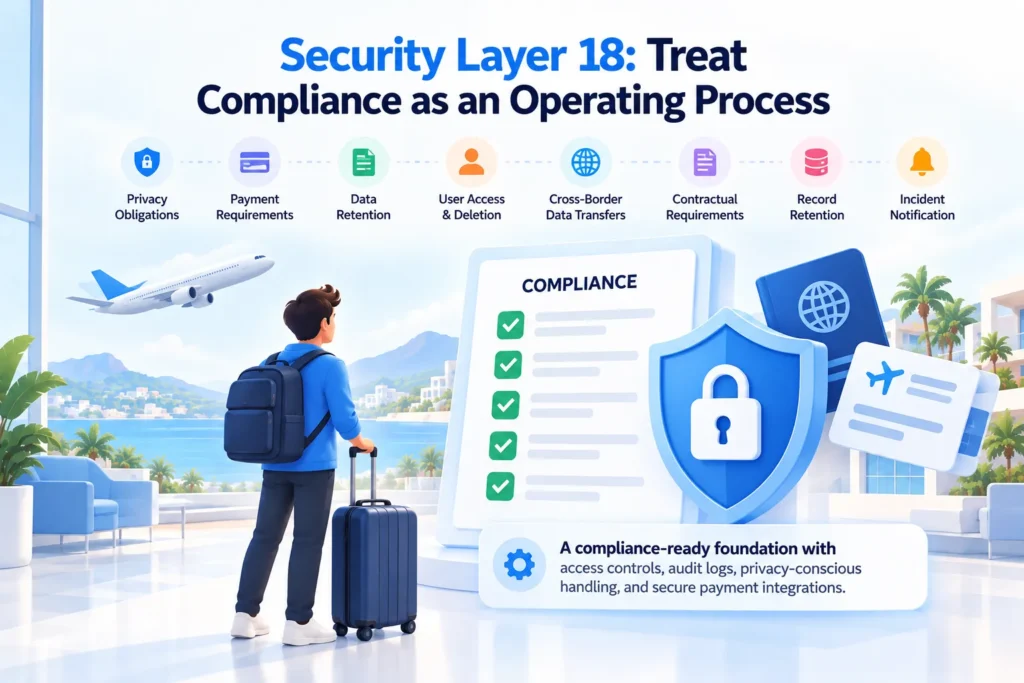
Security and compliance overlap, but they are not identical.
Depending on where the platform operates, founders may need to consider:
- Privacy obligations
- Payment requirements
- Data-retention rules
- User access/deletion requests
- Cross-border data transfers
- Corporate contractual requirements
- Record retention
- Incident notification
Avoid assuming that buying software automatically makes the business compliant.
The platform can provide a compliance-ready foundation and support controls such as access restrictions, audit logs, privacy-conscious handling, and secure payment integrations.
Final compliance still depends on jurisdiction, infrastructure, third-party providers, configuration, contracts, internal policies, and legal review.
B2B Travel Security Responsibilities by Layer
Who and What Needs Protection?
| Security Area | Main Risk | Key Controls |
|---|---|---|
| Agent Accounts | Account takeover, wallet misuse, unauthorized booking or refunds. | 2FA, role permissions, session controls, audit logs, step-up authentication. |
| Corporate Accounts | Cross-company data exposure and excessive employee permissions. | Organization isolation, RBAC, approval rules, offboarding, audit history. |
| Supplier APIs | Credential leakage, forged requests, manipulated booking data. | Server-side credentials, encrypted transfer, validation, rotation, adapter layer. |
| Payments & Wallets | Duplicate charges, unauthorized credits, refund abuse. | Server-side verification, ledger records, idempotency, controlled refunds. |
| Admin & Finance | High-impact privilege abuse or account takeover. | 2FA, least privilege, step-up verification, detailed action logs. |
| Operations | Untraceable manual changes and weak incident response. | Audit logs, alerts, monitoring, approval workflows, incident procedures. |
Founder Decision Signals
Agent Financial Authority
If agents can use credit, wallets, commissions, or refunds, authentication and financial audit controls should be treated as core product requirements.
Corporate Data Depth
If companies store employee travel, approval, billing, and expense information, organization-level isolation and role-based permissions become essential.
Supplier Dependency
If the booking business relies heavily on external supplier APIs, credential management, server-side integration, validation, monitoring, and failure handling deserve early attention.
Operational Privilege
If administrators can alter balances, refunds, commissions, or supplier settings, privileged actions should be restricted and auditable.
B2B Travel Platform Security Checklist
Before production, founders should verify:
- Agent roles are documented
- Corporate roles are documented
- Supplier roles are documented
- Administrator permissions are restricted
- Finance permissions are separated
- Two-factor authentication is available for privileged users
- Session revocation works
- Password reset flows are protected
- Agent balance changes are logged
- Credit limit changes are logged
- Commission changes are logged
- Refund activity is auditable
- Corporate records are isolated by organization
- Supplier credentials remain server-side
- Production and test credentials are separated
- API responses are validated
- Payment callbacks are verified
- Duplicate transaction handling exists
- Webhook replay protection is considered
- Sensitive data transfer is encrypted
- Admin access is reviewed periodically
- Former employees can be removed quickly
- Audit logs are protected
- Security monitoring is enabled
- Backups are tested
- Incident-response ownership is defined
Security is strongest when these controls are part of normal operations rather than a one-time launch checklist.
Mistakes Founders Should Avoid
Giving Every Agency Employee the Same Permissions
Booking agents, accountants, support users, and agency owners have different responsibilities. Shared high-privilege access increases unnecessary risk.
Putting Supplier Credentials in Frontend Code
Supplier keys and secrets should remain behind server-side services rather than being exposed to browser or mobile clients.
Allowing Financial Changes Without Audit History
Credit adjustments, wallet corrections, refunds, commissions, and payout changes should create traceable records that finance and operations can review.
Treating Corporate Isolation as a Frontend Filter
The backend must enforce organization ownership and permissions on each protected request. Hiding records in the interface is not sufficient access control.
Security problems often begin with broader product and operational decisions. This guide to common travel platform mistakes explains additional issues founders should address before scaling agent, corporate, supplier, and booking operations.
How Miracuves Supports B2B Travel Booking Platforms
Miracuves helps founders and travel businesses launch white-label booking platforms that can support traveler, agent, supplier, corporate, operations, finance, and administrative workflows.
Once agent roles, corporate workflows, supplier integrations, security controls, and customization requirements are clear, reviewing B2B travel platform development cost can help connect the required scope with budget planning.
For teams evaluating a launch-ready foundation, Miracuves’ B2B travel booking platform can provide a starting point for agent bookings, corporate travel operations, supplier connectivity, booking management, payments, statements, and administrative controls.
Teams comparing implementation partners can also review this guide to choosing a B2B travel development partner, especially when supplier integrations, access controls, payment workflows, and operational security are part of the rollout.
The security layer should then be configured around the actual operating model: which users can access corporate records, who can change agent credit, how refunds are approved, where supplier credentials are stored, what actions are logged, and what infrastructure controls are required.
Founders who want to understand the broader platform foundation can explore Miracuves’ travel booking platform software for traveler, agent, supplier, operations, finance, booking, and administrative workflows.
Businesses still comparing B2B, regional, or broader travel marketplace models can also explore Miracuves’ travel booking solutions before finalizing their security and operating model.
When the ready-made scope fits the rollout requirement, Miracuves can support 6-day solution delivery, giving founders more time to focus on supplier agreements, corporate onboarding, operating procedures, security configuration, and market validation rather than rebuilding common booking modules from zero.
Related reading: B2B travel booking platform architecture.
Final Thoughts: Secure the Authority Behind Every Booking
B2B travel platform security is not only about protecting passwords.
The more important question is what each authenticated user is allowed to do after login.
Agents may control customer bookings and credit. Corporate administrators may control employee data and travel policies. Suppliers influence inventory. Finance users manage statements and settlements. Platform administrators may control all of them.
That means security should follow authority.
Protect identities with strong authentication. Limit roles through least privilege. Keep supplier credentials server-side. Separate corporate data by organization. Log financial actions. Verify payments and callbacks. Monitor unusual activity. Remove stale access quickly.
The strongest platform is not the one with the longest list of security labels.
It is the one where founders, finance teams, and operators can answer three questions clearly:
Who accessed the system? What were they allowed to do? What did they actually change?
FAQs
Why does a B2B travel booking platform need stronger access controls?
B2B platforms can give agents, corporate administrators, suppliers, finance teams, and operators access to different data and financial functions. Role-based permissions help prevent users from accessing actions that are unnecessary for their responsibilities.
Should travel agents use two-factor authentication?
Two-factor authentication is especially useful for privileged agent accounts, finance users, administrators, and other roles that can change balances, refunds, commissions, or sensitive account settings.
How should corporate travel data be protected?
Corporate data should be isolated by organization, with backend authorization ensuring users can access only the company, department, employees, bookings, and financial information permitted by their role.
Where should supplier API credentials be stored?
Supplier credentials should generally remain in secure server-side configuration or secret-management systems rather than being exposed in mobile applications or frontend JavaScript.
How can an OTA protect agent wallets and credit limits?
Use an auditable financial ledger, restricted permissions, server-side validation, transaction history, credit-change logs, approval controls where appropriate, and step-up verification for high-risk actions.
Should payment success automatically confirm a B2B travel booking?
Not necessarily. Payment or credit authorization and supplier booking confirmation should be tracked separately because one can succeed while the other fails.
What should a travel-platform audit log record?
Useful records include role changes, credit adjustments, wallet transactions, commission changes, refunds, payout changes, supplier settings, corporate policy changes, booking overrides, and sensitive data exports.
Does buying a ready-made travel platform automatically make a business compliant?
No. A platform can provide security and compliance-supporting controls, but final compliance depends on the jurisdiction, deployment, integrations, data practices, contracts, internal policies, and legal review.
Miracuves is an independent software development company. We are not affiliated with, connected to, sponsored by, or endorsed by any company or product named in this article.
Terms such as “X Clone” are used descriptively. It is how the software industry refers to building a platform with functionality comparable to a known service, and how clients search for it.
The entire design and codebase of our products is built by our own team. Our products contain no code, design, graphics, or content originating from any third-party website or applications.
All third-party names and marks referenced in this article are the property of their respective owners, referenced solely to identify the services discussed.